
What Is Healthcare Compliance: How Integration Reduces These 3 Risks
What is healthcare compliance, and how can EMR integration help? Eliminate your medical practice's compliance risks with seamless EMR integration.
13 min read
In May 2023, a solo mental health provider agreed to pay OCR $15,000 over a single records request. A Florida primary care practice paid $20,000 after a patient’s daughter waited months for her late father’s chart. Both cases came down to records the practice couldn’t produce in time.
Small practices often assume HIPAA enforcement is aimed at hospitals and big data breaches. These settlements show otherwise. OCR goes after the everyday gaps too.
Those gaps rarely come from carelessness. A consent gets scanned into a shared folder under a file name nobody will search for.
A nurse gives prep instructions over the phone, then gets pulled into another call before charting them. A patient texts a photo of her insurance card to the office manager’s cell because that’s the number she has.
Each of those is a record someone meant to make. When your system depends on busy people logging everything by hand, some of those records will go missing.
That’s why EMR integration is a compliance lifesaver. When texts, reminders, intake forms, consents, and payments save to the chart as they happen, the record exists before anyone has to go looking for it.
Your staff stop rebuilding message histories from phones, inboxes, and binders every time an auditor or patient asks.
The sections below show where disconnected systems leave you exposed and what that costs, from the HIPAA penalty amounts that took effect in January 2026 to denied claims and staff turnover.
Fines get the headlines. A missing consent form or an unlogged text can also leave a chart incomplete, and that puts the next visit at risk.
HIPAA requires you to protect patient health information and to give patients access to their records. In practice, every message, form, and consent tied to a patient has to be secure, stored and accessible when a patient or auditor asks for it.
Larger groups often add SOC 2 Type 1 or Type 2 reports to the list. They usually require those reports from the vendors that handle their data.
Without EMR integration, each tool keeps its own record. Picture a reminder sent from a scheduling app, a consent signed on paper, and a follow-up text from a staff member’s cell phone. All three live in different places, and each is a spot where a record can go missing.
Here's where the gaps appear:
Picture your front desk at 7:45 a.m., retyping a stack of paper intake forms into the EMR before the first patient walks in. Every field typed twice is a chance to get it wrong. A penicillin allergy lands in the wrong box, or a new blood thinner never makes it onto the medication list.
Those slips can reach the exam room. A provider who trusts the chart may prescribe the very drug the patient flagged on paper.
They also leave a compliance gap. HIPAA’s Security Rule has an integrity standard: you must protect patient data from being changed or lost in error. When the chart doesn’t match the form the patient filled out, an auditor sees weak record-keeping.
A nurse calls a patient Friday afternoon: “No food after midnight before Monday’s procedure.” Nothing about that call goes into the chart. Texts sent from a staff member’s own phone and emails answered from a shared inbox usually end up the same way.
Auditors look for a record of patient instructions, reminders, and follow-ups. If you can’t produce one, an auditor can flag it as a compliance gap.
It also leaves you open in a dispute. Say the patient eats breakfast, the procedure gets canceled, and they say no one told them. With no log of that Friday call, it’s your word against theirs.
A patient signs a consent form at check-in. Someone scans it later that week, and it lands in a shared folder as “scan_0412.pdf” instead of in the chart. The file date now shows when it was scanned, not when the patient signed.
Paper has its own problems. The original might sit in a binder at the front desk, or at another office if the patient was seen there.
If you can’t find that form when you need it, you can’t prove the patient agreed. That gap hurts most with consent for procedures, telehealth visits, and financial agreements such as a payment plan. Each one needs the patient’s signed approval on file.
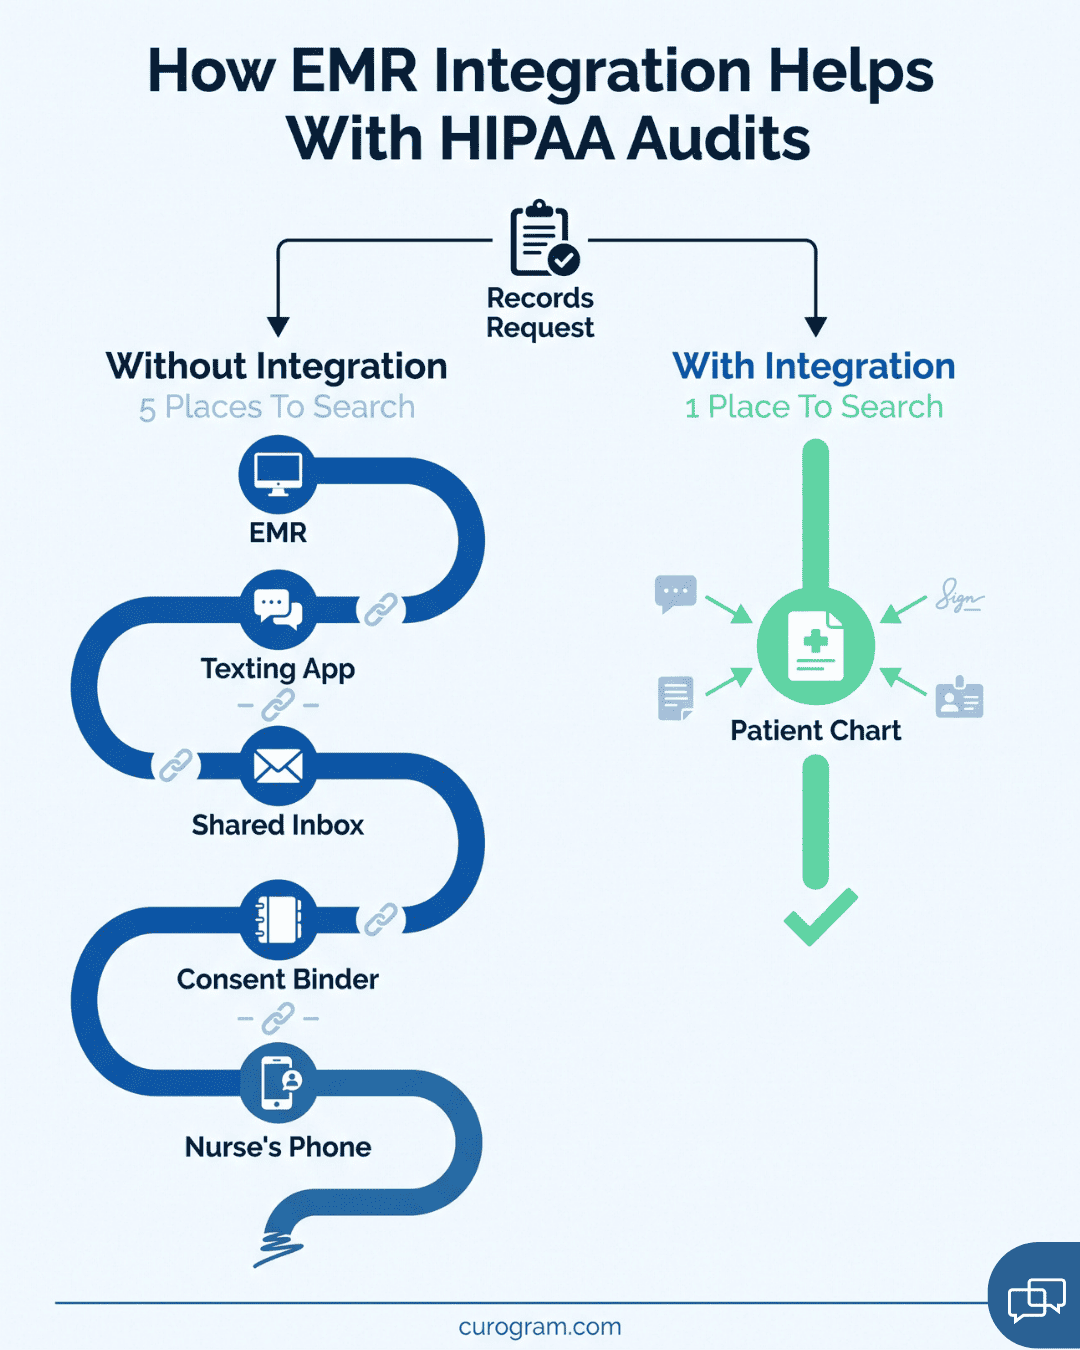
Say a patient asks for a copy of every message about last month’s billing dispute. Your staff start in the EMR, then check the texting app, the shared inbox, and the paper binder at the front desk. One reply is on a nurse’s personal phone, and she’s off until Thursday.
That search can eat hours. Under HIPAA’s right of access, you generally have 30 days to give patients their records. You get one 30-day extension, and only if you tell the patient why. Audit requests come with deadlines too.
Every place you search by hand is one more place a message can slip through. Miss the reply on that nurse’s phone, and the record you hand over is incomplete.
HIPAA fines went up again on January 28, 2026. HHS applied its annual inflation adjustment to HIPAA civil money penalties, effective that date. The amounts depend on how much the practice knew and whether it fixed the problem:
| What OCR finds | Fine per violation |
|---|---|
| You didn’t know | $145 to $73,011 |
| Reasonable cause | $1,461 to $73,011 |
| Willful neglect, fixed within 30 days | $14,602 to $73,011 |
| Willful neglect, not fixed | $73,011 to $2,190,294 |
Each tier has a yearly cap of $2,190,294 for repeat violations of the same rule.
Small practices get fined too. In May 2023, a solo mental health provider settled with OCR for $15,000 over a records request.
A Florida primary care practice paid $20,000 after a patient’s daughter waited months for her late father’s records. A North Carolina dental practice drew a $50,000 penalty for having no privacy official and no HIPAA policies.
Fines aren’t the only cost. Insurers and payers can deny a claim when the documentation behind it is missing, and you lose that payment on top of any penalty.
All four risks trace back to one habit: staff logging calls, texts, and forms by hand. That’s how you end up facing HIPAA penalties, denied claims, patient disputes, and reputational damage. Without EMR integration, every one of those records depends on someone remembering to enter it.

Most practices plan for the fine. Fewer plan for the denied claims, the staff hours lost to audit prep, the safety risk of a half-complete chart, or the patients who leave after a privacy scare.
Those costs repeat month after month, and each one in this section starts the same way: with a call, text, or form that never made it into your EMR.
Most practices plan for the fine. Fewer plan for the denied claims, the staff hours lost to audit prep, the safety risk of a half-complete chart, or the patients who leave after a privacy scare.
Those costs repeat month after month, and each one in this section starts the same way: with a call, text, or form that never made it into your EMR.
Say an auditor asks for every contact your practice had with one patient over the last six months. Your staff now have to rebuild the communication trails by hand.
They pull call logs that show dates but not what was said, dig through email inboxes, and flip through paper consent forms. Then they try to match it all against the EMR.
One request like that can eat dozens of staff hours. Those are hours your front desk and nurses aren’t spending with patients.
Running more than one location makes it worse. Each site may file consents, log calls, and handle email its own way. When the records from one office don’t line up with another’s, a missing piece is easy to overlook.
Every time someone retypes information, there’s a chance it comes out wrong. The odds go up when your front desk is entering forms between check-ins with the phone ringing.
A sulfa allergy gets skipped. A signed consent form sits in the scan tray and never gets attached to the chart.
These slips reach patients. A provider writing a prescription checks the allergy list in the EMR. If the allergy isn’t there, nothing stops the order.
They also draw regulators’ attention. When missing allergies and unfiled consents show up across many charts, an auditor sees a process that can’t keep records accurate, and that puts your practice at greater risk of enforcement.
A patient calls about her blood thinner before next week’s procedure. Your nurse tells her when to stop taking it, then gets pulled into another call. The note never makes it into the EMR.
On procedure day, the provider sees nothing in the chart about that call. If the patient stopped at the wrong time, or never got the message at all, she can end up with complications. And because the instruction isn’t on record, your practice carries the legal risk.
The cost of gaps like this is well documented. CRICO Strategies reviewed 23,658 malpractice cases from 2009 to 2013 and found communication failures played a part in 30% of them.
Those cases added up to $1.7 billion in malpractice costs and 1,744 deaths. Poor documentation and incomplete informed consent were among the most common breakdowns.
Many patients now want communication via text, along with email and a patient portal. When your systems can’t keep up, your staff find their own workarounds.
A patient texts a photo of her insurance card to the office manager’s cell because that’s the number she has. A billing question gets answered from a personal Gmail account.
IT teams call this “shadow IT”: tools your staff use that nobody approved or set up to protect patient data. Messages sent this way never reach the EMR.
That’s a problem under HIPAA’s Security Rule, which requires audit controls that record activity in systems holding patient data. A personal phone keeps no such log. If an auditor or patient asks what was said, you have nothing to show them.
HIPAA doesn’t let a breach stay quiet. If unsecured patient data is exposed, you have to send a notice to every affected patient.
A breach involving 500 or more people also gets listed by name on HHS’s public breach portal. If 500 or more residents of one state are affected, you have to alert local media too.
OCR posts its settlements and penalties online as well, with the practice’s name attached. For a small practice, that public record can hurt more than the fine.
Patients who get a breach letter start to wonder what else is at risk. A nearby practice with a clean record looks like the safer pick.
Each patient who leaves takes every future visit and referral with them. Winning that trust back can take years.
Without integration, compliance turns into a stack of manual chores on top of your staff’s real jobs. Someone has to chase unsigned consent forms, type call notes into the chart, and recheck intake entries against the paper copy. Day after day, this administrative pressure contributes to burnout and turnover.
Replacing a staff member costs real money. The Center for American Progress reviewed 30 case studies and found the typical cost of turnover was 21% of a worker’s yearly salary. For example, a front desk role paying $40,000 would cost about $8,400 to replace.
What that person knew leaves with them, too. They knew which binder holds last year’s consents and which patients only answer by text. The new hire is still learning those workarounds, so mistakes become more likely right when you’re already short-staffed.
Manual compliance work also limits how far your practice can grow. Opening a second location means another set of binders, inboxes, and call logs for your staff to track. Adding telehealth brings its own consent forms to chase.
Value-based care makes the gap more expensive. Programs like Medicare’s MIPS tie part of your payment to the quality data you report. Pulling that data takes longer when your records sit in several different places.
Your managers feel this most. A week spent rebuilding records for an auditor is a week they can’t spend hiring, planning a new service, or working with payers.
Every cost in this section feeds the next one. Fines and denied claims cut your budget, burnout raises turnover, and new hires make more mistakes. Without EMR integration, keeping your records complete depends on your staff remembering to log every call, text, and form by hand.
With EMR integration, the record gets made when the work happens. A reminder goes out, a patient signs a consent form, a payment comes in, and each one lands in the patient’s chart on its own. Nobody on your staff has to remember to log it.
Curogram works this way. Our platform connects patient texting, reminders, intake forms, and payments with your EMR. Every message and form is encrypted, time-stamped, and saved in the chart, right where an auditor will look for it.
When a patient fills out an intake form online, their answers go straight into the EMR. So do reminder replies and patient texts. Your front desk no longer has to retype a stack of forms before the first appointment.
That removes the step where most typos happen. If a patient lists a sulfa allergy, the provider sees exactly what the patient entered.
Signed consent forms attach to the chart too. That means no scan tray for them to get lost in, and no gap for an auditor to find later.
Our two-way texting is HIPAA-compliant and gives patients one practice number to text. Photos of insurance cards and questions about procedure prep stop landing on staff members’ personal phones.
Each message is encrypted, time-stamped, and tied to the patient’s record. That gives you the log you’d otherwise have to piece together by hand. When an auditor asks what was said to a patient and when, your office manager opens the patient’s record and the whole thread is there, with dates and times.
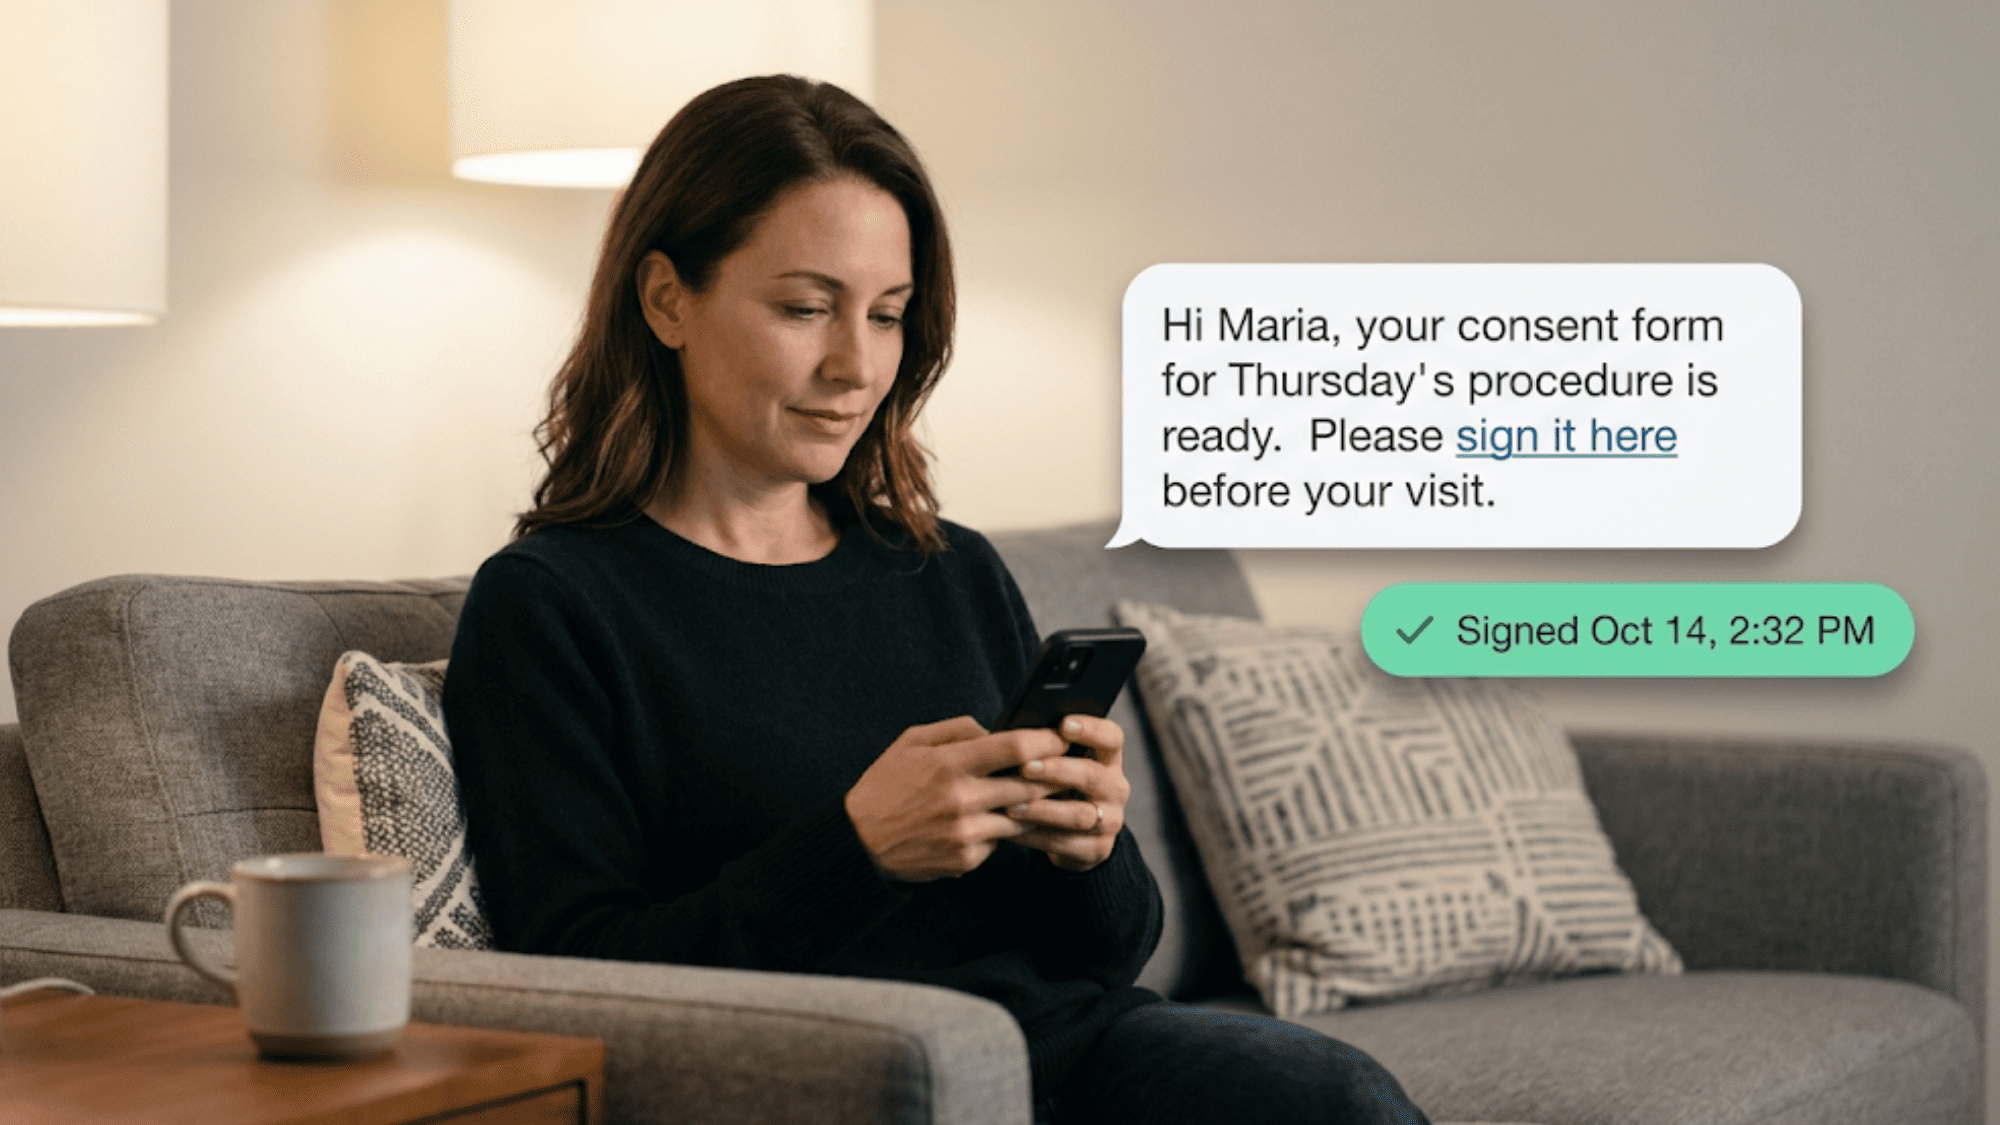
We send patients digital consent forms they sign electronically. Each signed form is time-stamped and saved to the patient’s chart in the EMR.
That time stamp records the moment the patient signed. Nobody has to scan the form later, so there’s no file date to confuse with the signing date.
It counts most for consents you can’t afford to lose, like surgery and telehealth. If a patient later questions what they agreed to, you can open the chart and show the signed form with its date and time.
A patient who misses a follow-up can go months without the care their provider ordered. If something goes wrong in that gap, you may need to show you tried to reach them.
Curogram reminders pull the appointment details and prep instructions from your EMR and text them to the patient. The patient replies to confirm or asks to reschedule, and each reply is logged. That log shows when you reminded the patient, what you sent, and how they answered.
Fewer patients miss visits, too. Based on our internal data, Atlas Medical Center cut its no-show rate from 14.20% to 4.91% in three months. Across our clients, the average appointment confirmation rate is above 75%.
Our online forms collect patient information before the visit. Patients can also upload photos, like the front and back of their insurance card, through an encrypted link.
That gives patients a safe place to send what they’d otherwise text to a staff member’s cell. The photo is saved to the patient’s record in the EMR, alongside the rest of their intake, so it’s easy to find during an audit.
Every patient who finishes intake online is one less clipboard for your front desk to retype and file.
Payments leave a paper trail too, and it’s easy to lose. A patient reads a card number over the phone, and someone jots it on a sticky note to run later. Now that note holds the patient’s card details, and nothing ties the payment to their chart.
With text-to-pay, we text the patient an encrypted payment link. They pay from their phone, and the transaction posts back to your EMR with the date and amount.
When a patient later says, “I already paid that,” your billing team can open the record and see the payment. No card numbers get written down or passed between staff.
Go back to that auditor asking for six months of contact with one patient. When texts, reminders, consents, forms, and payments are saved to the chart, most of that request already sits in one place. Your staff pull it from the patient’s record without digging through inboxes or the consent binder.
Phone calls still need notes. For those, the record is only as complete as what your team types in.
If you run several locations, every site logs the same way on the same platform. A manager can check records for any office from one dashboard.
Remember the chores from earlier: chasing unsigned consents, typing call notes into the chart, rechecking intake against paper. When texts, forms, consents, and payments save to the chart on their own, most of that list goes away. Phone calls still need a note, but that’s one task left out of four.
The phones get quieter, too. Based on our internal data, automated texting has cut inbound calls by 24%, with some practices seeing phone volume drop by up to 50%. Front desk productivity has gone up 30% or more.
Less busywork also means less of the pressure that pushes staff to quit. And your records no longer depend on one careful employee. When that person takes a vacation or leaves, the chart keeps filling in.
Healthcare regulations are evolving. From SOC 2 to payer-specific mandates, requirements will only grow stricter. Curogram is designed to adapt, ensuring clinics stay compliant with new standards. By integrating now, clinics are not just solving today’s issues but preparing for tomorrow’s new set of challenges.
Curogram connects with nearly any EMR. Patient texts, reminders, intake forms, consents, and payments go into the chart, encrypted and time-stamped. Testimonials from providers point to the same results: fewer no-shows, faster confirmations, and calmer audits.
Our internal data backs up the first two. Across our clients, no-show rates run 53% below the industry average, and the average confirmation rate is above 75%. Covina Arthritic Clinic confirms more than 1,100 appointments a month through our platform.
For your practice, that means:
Most compliance gaps start with a record someone meant to make. A call note never gets typed. A consent sits in the scan tray. An insurance card lands on a manager’s personal phone.
Busy staff skip steps, and any system that depends on them logging everything by hand will have holes. The fewer records your team has to create manually, the fewer will be missing when an auditor, payer, or patient asks for them.
That’s what EMR integration fixes. When texts, reminders, forms, consents, and payments save to the chart as they happen, the record exists before anyone has to go looking for it. Your staff still write call notes, but they stop chasing everything else.
Curogram connects with nearly any EMR, so you can start with the system you already use. Book a demo to see how your patient texts, forms, and payments would land in your EMR, and what your next records request would look like.
What is healthcare compliance, and how can EMR integration help? Eliminate your medical practice's compliance risks with seamless EMR integration.
Disconnected EMR systems create costly inefficiencies. Learn the risks and why integration is essential.
Connect your EMR to a communication platform and ask four questions first. Of 126 EMRs we track, 67 are ready today and 42 write appointment statuses...