
Why EMR Integration Is a Compliance Lifesaver
EMR integration boosts compliance and protects patient data. Learn why it’s a HIPAA lifesaver.
9 min read
Most compliance problems don't start with an obvious mistake. They start with something small, like a quick text from a staff member's personal phone or a consent form that never got scanned.
Nobody meant to break a rule. They were trying to help a patient quickly.
That's the hard part about compliance in a busy clinic: your team handles calls, texts, forms, and payments across several tools every day. When those tools don't talk to each other, details slip through the cracks, and each missing detail becomes a gap an auditor or payer can find.
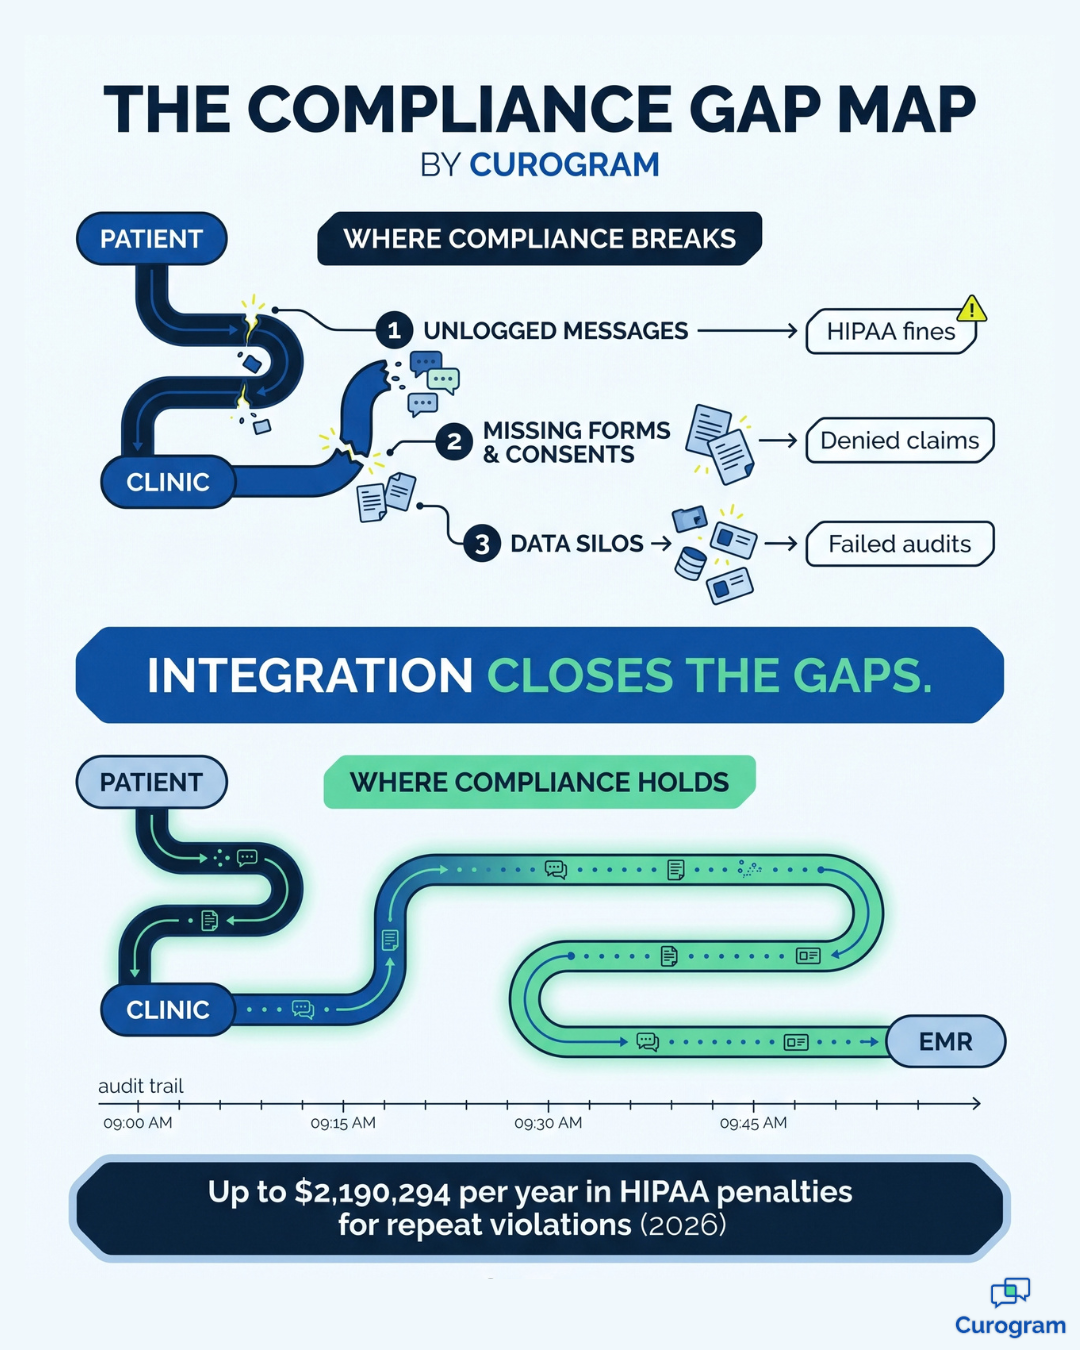
Those gaps add up. An unlogged message can start an investigation, and one missing consent can turn a paid claim into a denied one. Over a year, these small misses can cost your clinic thousands of dollars, hours of staff time, and patient trust.
So, what is healthcare compliance, and why does it feel so hard to keep up with? At its core, it means following the rules that protect patient data, guide billing, and support patient safety. The rules are clear enough; the trouble is that disconnected systems make it difficult to prove you followed them.
In this guide, you'll learn about the three healthcare compliance risks that cause the most damage in clinics today. You'll discover what each one costs, why manual fixes rarely hold up, and how integration closes the gaps for good.
You'll also see how Curogram connects patient communication to your EMR, so every reminder, form, and payment request is automatically logged where it belongs. Instead of depending on staff memory, your records stay complete on their own.
By the end, you'll understand where your clinic's biggest risks are hiding. You'll also know what it takes to fix them before an auditor discovers them first. Let's start with the basics.
Healthcare compliance means following the rules that protect patient data, keep billing honest, and support safe care. These rules include HIPAA, SOC 2 standards, CMS rules, and payer-specific requirements. Some are federal laws. Others are standards and contract terms that payers and partners expect you to meet.
Compliance isn't optional. It's central to patient trust and to keeping your clinic open. When you fall short, the results can include fines, denied claims, lawsuits, and a damaged reputation.
One of the biggest compliance risks is communication outside secure, integrated systems. Staff often resort to personal phones, Gmail accounts, or standalone messaging apps to reach patients quickly. While convenient, these channels lack encryption, audit trails, and EMR integration.
As a result, important details aren’t documented, and sensitive data may be exposed. Regulators view this as a HIPAA violation, and patients see it as a breach of trust.
During audits, the inability to prove what was communicated and when becomes a liability. A missing record of a reminder, instruction, or consent can be flagged as non-compliance. Integration solves this by centralizing communication in one HIPAA-compliant platform that automatically logs every message into the EMR, creating a permanent audit trail.
Documentation gaps are another compliance risk in healthcare. Intake forms may be misplaced, consents improperly filed, or reminders left undocumented. In disconnected workflows, paper forms are scanned inconsistently, and verbal instructions often vanish without record. These gaps make it nearly impossible to defend care decisions or billing claims.
For example,
A payer may deny a claim if a consent cannot be produced, or a malpractice claim may turn against a clinic if instructions weren’t documented. Integration eliminates this risk by digitizing intake, consents, and reminders.
Forms completed by patients sync automatically into the EMR, and every reminder or confirmation is time-stamped and logged. Clinics gain confidence knowing nothing is missing.
Finally, disconnected EMRs themselves create compliance issues. Many EMRs don’t natively handle patient communication, forcing staff to use external tools. The result is data silos where some information lives in the EMR, while other critical communication lives elsewhere. This makes audits difficult and increases the likelihood of overlooked details.
Integration closes the loop by ensuring all communication flows back into the EMR. Every text, reminder, intake form, and payment record is attached to the patient chart. This not only satisfies regulatory requirements but also reduces the workload on staff. Instead of acting as “human middleware,” staff rely on automation to keep records complete and compliant.
These three compliance risks are completely preventable. With integration, compliance shifts from being a staff-dependent burden to a system-ensured safeguard. In short, integration doesn’t just help clinics stay compliant; it makes compliance automatic.
Compliance risks aren't abstract. Every unsecured message, missing form, or undocumented instruction creates real exposure. Here's how those risks hit your finances, your team, and your reputation.
HIPAA fines are steep, and HHS raises them each year to keep pace with inflation.
Here's what the 2026 penalty ranges look like for each violation:
| Level of fault | Penalty per violation |
|---|---|
| No knowledge of the violation | $145 to $73,011 |
| Reasonable cause | $1,461 to $73,011 |
| Willful neglect, fixed within 30 days | $14,602 to $73,011 |
| Willful neglect, not fixed in time | $73,011 to $2,190,294 |
The yearly cap for repeat violations of the same rule can reach $2,190,294, though HHS has applied lower caps to less serious cases since 2019. In practice, one careless habit repeated across many patients can turn into a six- or seven-figure problem.
Fines aren't the only cost. A single unsecured message can spark an investigation that drains thousands in legal fees. Missing documentation also leads to denied claims, since payers hold back payment when you can't produce a required consent.
Here's an example of how that adds up. If your clinic loses 5 claims a month at $200 each because of missing paperwork, that's $1,000 a month, or $12,000 a year (illustrative example).

Disconnected systems force your staff into constant compliance firefighting. They spend hours hunting for consents, piecing together message trails, and retyping intake forms. Every one of those hours could go toward patient care or tasks that bring in revenue.
For a small team, this adds up fast. In some clinics, compliance busywork can take up as much as 20% of the weekly workload. On a five-person front desk working 40 hours each, that's 40 hours a week, or the same as one full-time employee (illustrative example).
Audits are stressful enough on their own. With fragmented workflows, they become overwhelming. Staff scramble to pull together phone logs, scanned folders, and screenshots to prove compliance.
This reactive approach often leads to errors or missing evidence. An audit that should take hours can drag on for weeks, wearing out your team and causing costly delays.
Patients expect their data to be safe. News of a HIPAA violation spreads quickly, eroding confidence and pushing patients to switch providers. Online reviews spread the damage further and make it harder to attract new patients.
Reputation damage also lasts longer than any fine. Once trust is broken, rebuilding it can take years. In a competitive market, you can't afford to lose credibility over a communication failure you could have prevented.
Compliance isn't just paperwork. It's tied directly to patient safety. If instructions aren't documented or consents are missing, your risk in a malpractice claim goes up.
Courts look at documentation to decide who was responsible. Without a record, they often assume the clinic didn't do its part. Integration protects you by making sure instructions and consents are always logged.
Constant firefighting leads to burnout. Staff who juggle disconnected systems feel overwhelmed and undervalued, and many eventually leave.
Turnover is expensive. Replacing an employee can cost 20% to 30% of their yearly salary. For a front desk role paying $40,000, that's $8,000 to $12,000 per hire (illustrative example). Knowledge gaps during the handoff also raise compliance risk, while strong systems help you keep good people longer.
Compliance risk also puts a ceiling on growth. When your team is buried in manual compliance tasks, there's little room to add services or open new locations. Leaders spend their energy putting out fires instead of planning ahead.
Clinics with integrated systems can grow with more confidence. Compliance is built into how they work, so each new location doesn't bring new risk.
These problems don't happen in isolation. They feed into each other. Unsecured messages lead to missing records, which lead to denied claims and lost revenue. Lost revenue limits hiring, which deepens burnout and leads to even more errors.
The cycle repeats until something breaks it. Integration is what breaks it.
|
Pick five recent patient visits at random. For each one, try to pull up the appointment reminder, signed consent, intake form, and any payment request from a single system. If any record takes more than a few minutes to find, or lives in a personal inbox, a paper folder, or a separate app, you've found a compliance gap. Those are the same gaps an auditor or payer will look for first. |
EMR integration turns compliance from a manual chore into a built-in safeguard. When reminders, messages, intake, billing, and records connect directly to your EMR, every action is logged, secure, and easy to find. Curogram is built to do exactly that.
Curogram’s HIPAA-compliant texting encrypts every message and stores it with time stamps tied to patient records. Whether it’s a reminder, confirmation, or follow-up, the message is logged automatically. This eliminates the risk of unsecured or undocumented communication and ensures a permanent audit trail.
Curogram digitizes intake and consent workflows. Patients complete forms on their devices, sign electronically, and upload insurance cards securely. Data flows directly into the EMR, eliminating scanning, filing, or retyping. Each form is stored with timestamps, ensuring compliance documentation is airtight and instantly retrievable.
No-shows create both revenue and compliance risks. Missed follow-ups can be seen as lapses in continuity of care. With Curogram reminders, patients receive personalized, EMR-synced instructions at the right time. Confirmations and reschedules are logged automatically, ensuring compliance with outreach requirements.
Billing workflows are also tied to compliance. Missing financial documentation creates liability. Curogram’s text-to-pay sends secure payment requests and logs every transaction back into the EMR. This reduces A/R cycles, strengthens cash flow, and creates a complete financial audit trail.
With integration, every reminder, message, form, and payment is logged in one place. Audits that once took days now take minutes. Administrators can generate reports instantly, confident nothing is missing. For multi-site clinics, compliance records are unified across locations, creating consistency and scalability.
Integration reduces the need for staff to manually log communications or chase missing documents. By automating compliance, staff regain hours weekly. This improves morale, reduces turnover, and ensures compliance doesn’t rely on overworked employees.
The rules keep changing. From HIPAA updates to new payer demands, they tend to get stricter over time. Curogram is designed to adapt as standards change, so compliance becomes a safeguard for tomorrow, not just a box you check today.
The results show up in daily operations. Curogram clients average an appointment confirmation rate above 75%, and their no-show rates are 53% lower than the industry average. Atlas Medical Center, for example, cut its no-show rate from 14.20% to 4.91% in just three months. Fewer missed visits means fewer gaps in care to explain and a cleaner record of every patient touchpoint.
Integration stops compliance risks at the source. It also helps you build patient trust and frees your staff to focus on care.
Here's what you can expect from a connected compliance management system:
The three biggest healthcare compliance risks are unsecured communication, missing documentation, and EMR data silos. They look like separate problems, but they share one root cause: disconnected workflows.
Unsecured channels like personal texting or regular email expose your clinic to HIPAA violations and fines. Missing or incomplete records leave gaps that put claims, audits, and even patient safety at risk. And data silos turn your staff into "human bridges" who retype information between tools while key details slip away.
Left alone, these risks feed each other. Denied claims shrink your revenue. Burnout drives turnover. A single gap you could have prevented can lead to penalties and losses that cost far more than fixing the system ever would.
The fix doesn't require more effort from your team. It requires better connections between the tools they already use. When communication, intake, reminders, and payments flow into your EMR, your records stay complete without anyone having to chase them down.
That's exactly where Curogram comes in. It connects patient communication to your EMR, logs each interaction, and keeps sensitive information behind secure links. You lower your exposure to costly risks while also saving staff time, protecting revenue, and building patient trust.
If your clinic still relies on disconnected tools, now is a good time to look closely at where your gaps are. Start with the quick audit check above, and note every record that took too long to find or lived outside your EMR. Then think about how much time your team spends proving compliance instead of delivering care each week.
You don't have to wait for the next audit or denied claim to find out what's missing. See how Curogram connects compliance to your EMR in a personalized demo and learn how integration can turn compliance into one of your clinic's strengths.
EMR integration boosts compliance and protects patient data. Learn why it’s a HIPAA lifesaver.
 Aubreigh Lee Daculug : 8/7/26, 6:00 PM
Evaluate secure texting platforms for your medical practice: HIPAA compliance, EMR integration, pricing, patient experience, and more.
 Mira Gwehn Revilla : 9/30/26, 9:00 AM
Learn how multi-location outpatient practices can implement HIPAA-compliant two-way texting with clear governance, EHR integration, and rollout steps.