Everything You Need to Know About Patient Engagement and HIPAA Compliance
Patient engagement and HIPAA compliance go hand in hand to achieve improved health outcomes and establish secure transmission of medical information.
6 min read
Paul Dumayac : Published Updated
A nurse posts in the clinic's #front-desk channel: "Mrs. Alvarez in room 3 says her new BP med is making her dizzy. Can someone pull her chart?" Three people react with a thumbs up. Nobody asks whether that message should be in Slack.
Many practices already use Slack for scheduling swaps, supply runs, and shift chatter. The trouble starts when a patient's name and a health detail show up in the same message.
So, is Slack HIPAA compliant? It can be, on Slack's top enterprise plan, with a signed business associate agreement and extra tools the practice sets up itself. Even then, Slack's own rules bar using it to talk with patients.
This guide covers what HIPAA requires of a messaging tool and what Slack asks of healthcare customers. It also covers where Slack stops being useful and what to look for in a tool that reaches patients.
Our view: for most small and mid-size practices, Slack is a fine tool for non-clinical staff chat. Keep PHI out of it unless your organization has done the full enterprise setup.
HIPAA sets the rules for how practices and health plans protect patient health data. Any vendor that handles that information for them has duties too.
Protected health information, or PHI, is health information tied to a person. HIPAA lists 18 details that turn health data into PHI, including:
A Slack message with a patient's first name and room number plus a symptom counts. So does a screenshot of a schedule.
A vendor that stores or transmits PHI for a practice is a business associate. HIPAA requires a written business associate agreement (BAA) before the vendor gets any PHI. The BAA sets out how the vendor protects the data and reports breaches.
The Security Rule's technical safeguards apply to the tool itself. That means a login for each user, activity logs, and protected data in transit. Since a 2013 rule change, vendors can be fined directly, along with the practice.
Fines were adjusted on January 28, 2026 and run from $145 to $2,190,294 per violation, depending on the level of fault.
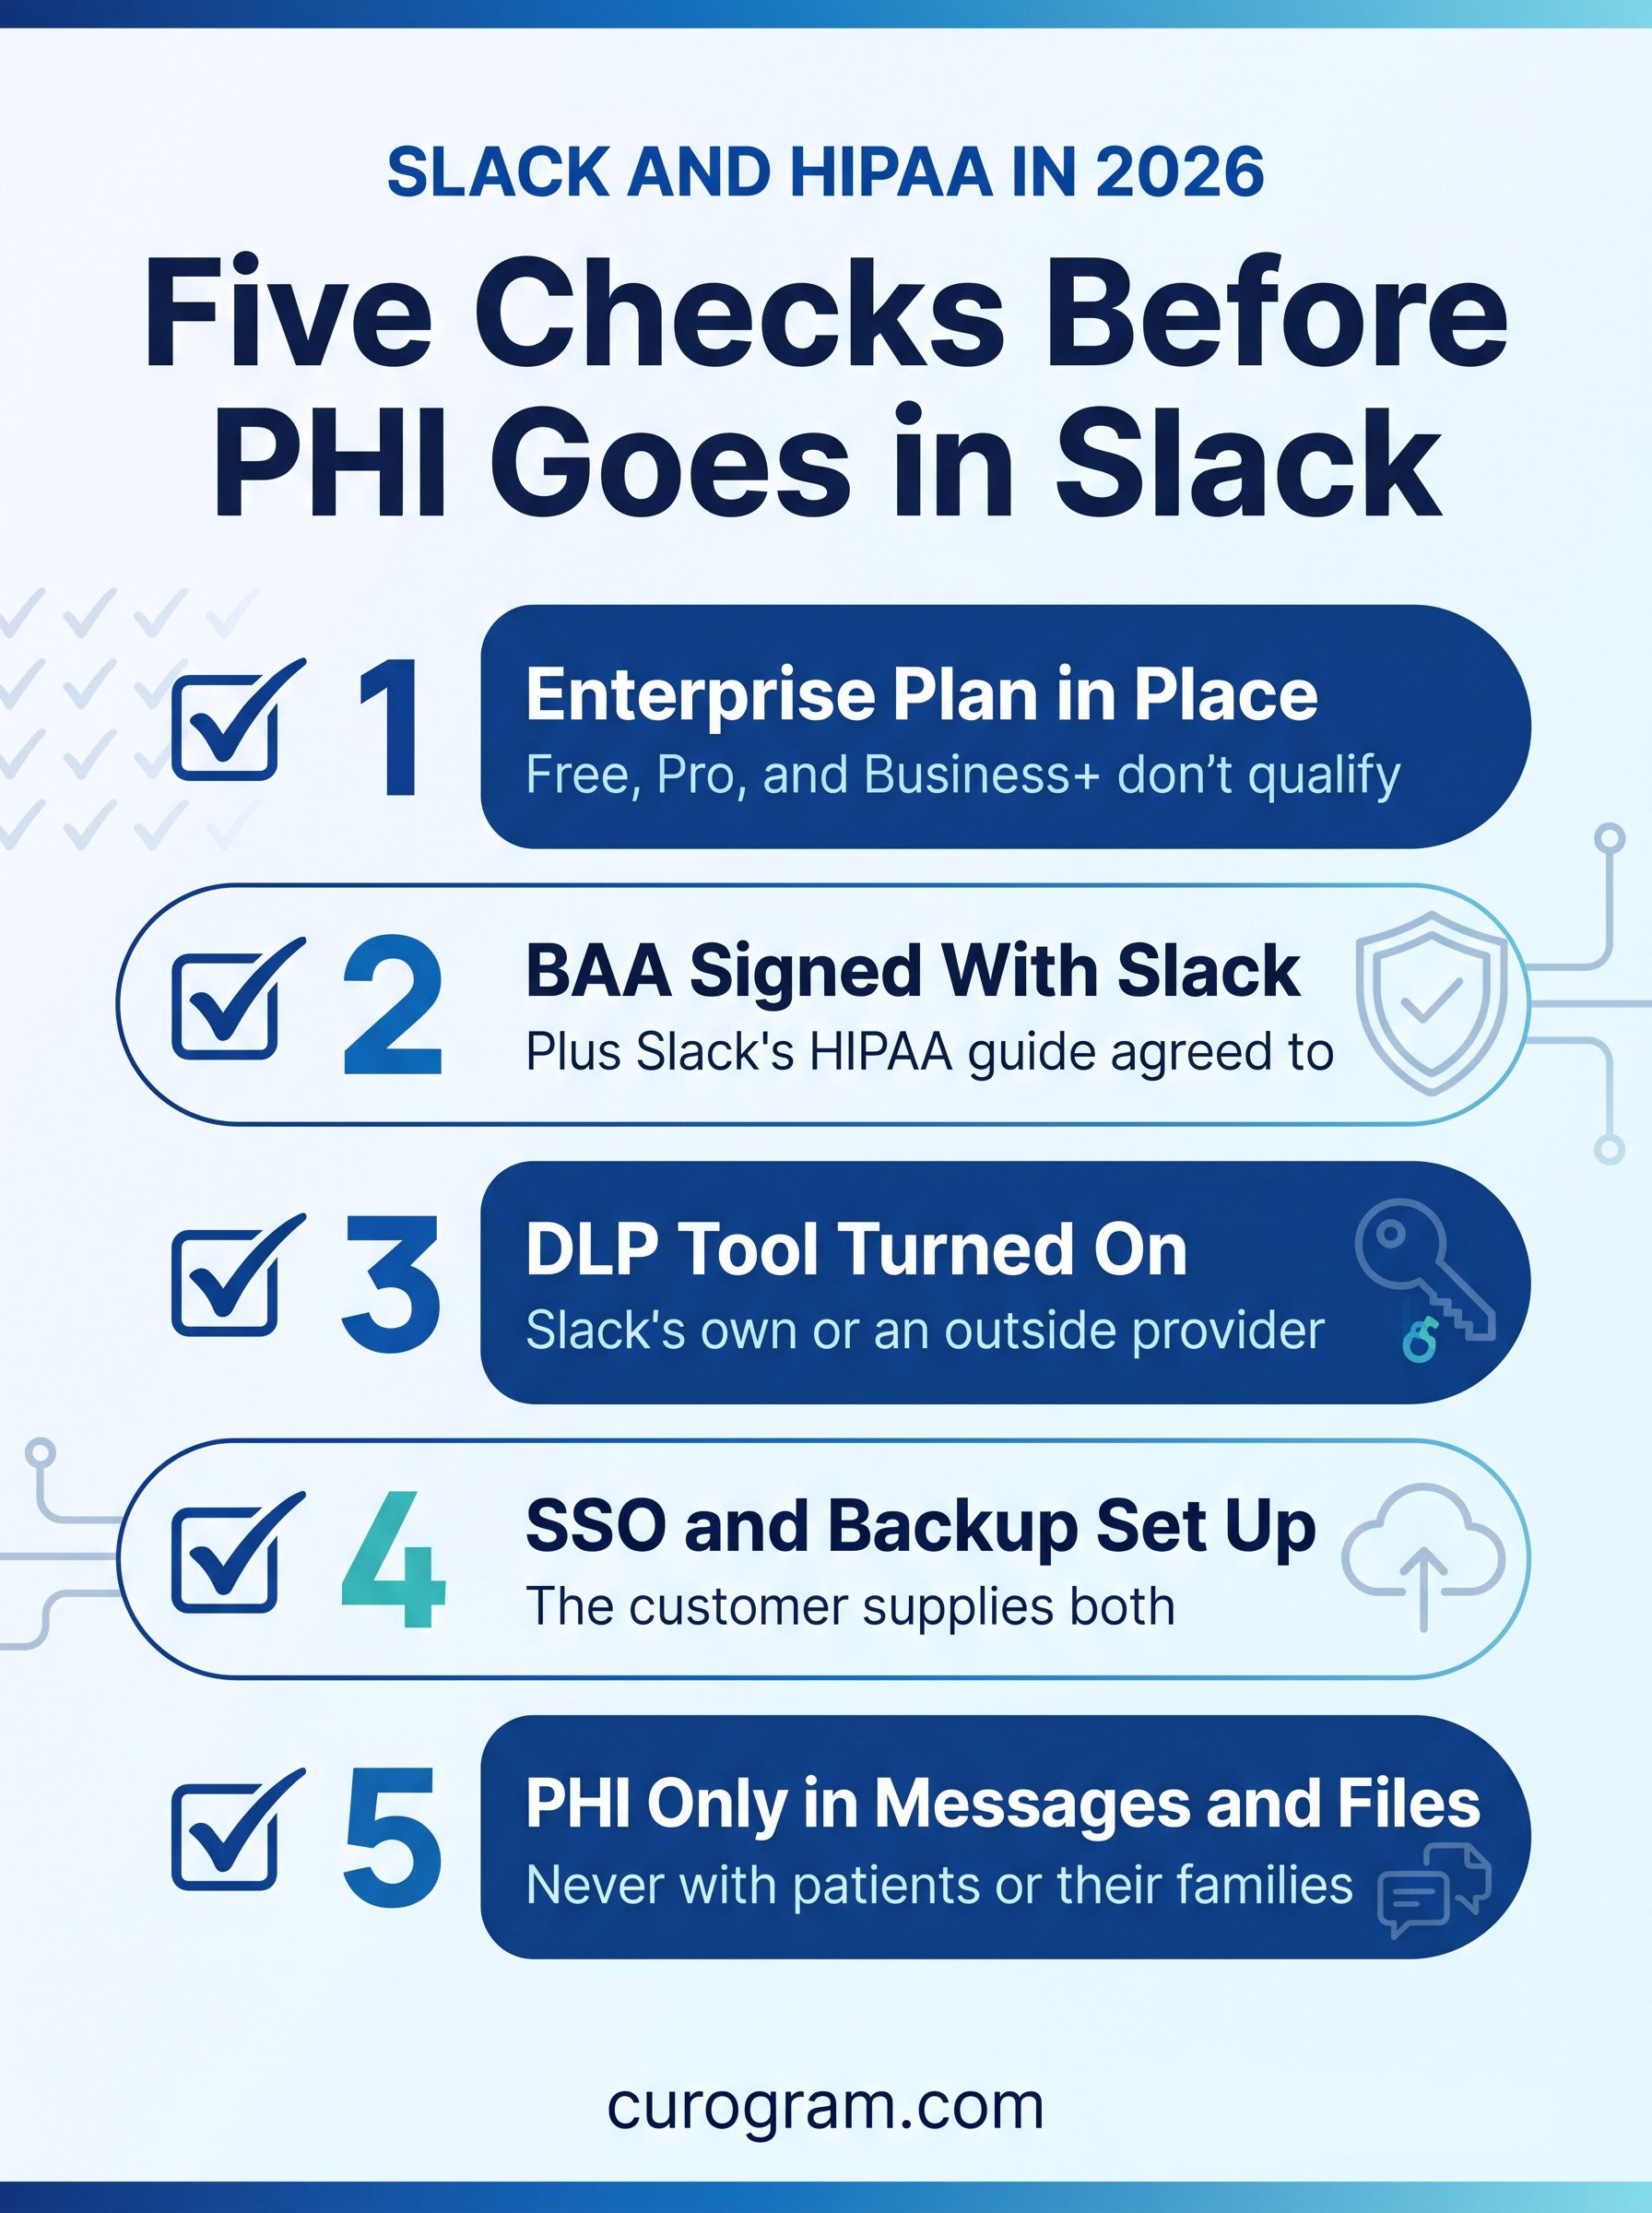
Slack's HIPAA support sits on one plan. Its pricing page lists HIPAA support only on Enterprise+, the top tier. The help pages call it the Enterprise plan, and older material calls it Enterprise Grid.
According to Slack's HIPAA help article, a healthcare customer must:
Its HIPAA overview adds two more pieces the customer must supply. One is a single sign-on (SSO) tool, and the other is a backup or archive tool. The customer also gives Slack a list of every workspace where PHI will appear.
Even with a BAA, PHI can go in only three places. Those are messages, files and file names, and the names of private channels or direct messages. Slack says it may not go in other features.
Email forwarding into Slack is turned off for HIPAA customers. Channels shared with outside organizations need extra controls, and channels with PHI should be private.

The enterprise setup works for large health systems with IT teams. For a practice with 15 staff and no security team, it raises hard questions.
Enterprise+ is sold through Slack's sales team, with no public price. The plan covers the BAA, but the practice still has to buy, set up, and watch a DLP tool, an SSO tool, and an archive.
Each outside tool that touches PHI may need its own BAA. A practice that adds a scheduling bot or a note-taking app has to check every one.
And someone has to read the DLP alerts. A rule that flags a birth date or medical record number in a public channel only helps if a person acts on it.
Slack signs a BAA only for enterprise customers who agree to its HIPAA guide. Before signing, ask three things: which workspaces it covers, which features it excludes, and who handles breach notice.
Keep the signed copy with your HIPAA records. HIPAA requires practices to keep policies and agreements for six years.
Slack's help article is direct: "You may not use Slack to communicate with patients, plan members, or their families or employers." Patients can't be added as members or guests.
That rules out Slack for reminders, intake forms, results notices, and video visits. A practice still needs a separate, HIPAA-ready tool for every message to patients.
Patients now expect to handle routine tasks by phone. Confirming a visit, sending an insurance card photo, or joining a video follow-up from work all happen outside the office.
Texts reach almost everyone. 98% of U.S. adults own a cellphone, per Pew Research, and a reminder that lets a patient reply "C" to confirm saves a call for both sides.
Video visits fill the gap for follow-ups that don't need an exam. A 10-minute medication check by video saves an older patient a ride and a half day.
Slack handles staff talk. A tool that can't send a reminder, collect a form, or start a video visit leaves all of that work on the phone.
A HIPAA-ready tool for patient communication should cover four needs. Each one ties to a daily front desk task.
Patients shouldn't need an app download or a portal password. A secure link sent by text that opens in the phone's browser works for patients who struggle with apps.
Practices on eClinicalWorks can see how secure texting works with eCW. It covers reminders and messages that keep PHI behind a secure link.
Staff should work from one screen that shows patient messages, video visits, and forms together. The tool should pull the schedule from your EHR so nobody retypes appointments.
Online forms belong in the same place. Our guide to HIPAA-compliant online forms for athenahealth users covers what to check when forms replace clipboards.
Staff will message each other about patients no matter what tool you give them. If the approved tool can't handle it, they'll use personal texts or a consumer app.
Pick a platform where staff can message each other inside the same system that holds patient conversations, with a BAA covering both.
Ask for the BAA before the demo ends. Then confirm the tool keeps message history you can pull for an audit.
Curogram works alongside your EHR to handle patient texting, forms, and video visits in one place.
Curogram Highlight: 2-Way Texting From Your Main NumberCurogram's 2-Way HIPAA-Compliant Texting runs from your practice's main phone number. Messages with PHI go out as encrypted links, and patients don't need an app or a password. Patients can confirm appointments, reply with questions, and fill out forms on their phones, including insurance card photos. Staff can message each other in the same platform, and after-hours auto-replies tell patients their text was received. Curogram keeps message history as an audit trail. It's HIPAA-compliant and SOC 2 Type II certified, and patients can join video visits from a text link with no download. |
Slack can support HIPAA on its enterprise plan, with a BAA, outside DLP and SSO tools, and strict limits on where PHI goes. It can't be used with patients at all.
For most practices, that makes Slack a staff tool for non-clinical chat. Patient messaging needs a separate platform built for it.
This week, check your Slack workspace for any channel where patient names appear. Then decide whether to complete the enterprise setup or move those conversations to a tool with a signed BAA.
Want one place for patient texts, forms, and staff messages? Book a demo with Curogram and we'll show HIPAA-compliant texting working with your EHR.
Only Slack's top plan, called Enterprise+ on its pricing page and Enterprise Grid in older material. The Free, Pro, and Business+ plans don't support HIPAA, and Slack won't sign a BAA for them.
Slack's HIPAA terms bar using Slack to talk with patients, plan members, or their families. Patients can't be added as members or guests. A practice needs another tool for every message to patients.
Keep patient names, dates, and health details out of Slack entirely. Use Slack for shift swaps and supply chat. Move patient talk to a tool with a signed BAA, and remind staff that screenshots count too.
Look for a signed BAA and patient texting with no app. Online forms, video visits, and staff messaging should be in the same tool. It should pull your schedule from your EHR and keep message history for audits.
Patient engagement and HIPAA compliance go hand in hand to achieve improved health outcomes and establish secure transmission of medical information.
Is WhatsApp HIPAA Compliant? Learn how America's leading healthcare providers are deploying and operating profitable & streamlined telemedicine...
Looking for Weave alternatives? Compare features, pricing, and HIPAA compliance to choose the best patient communication platform.